

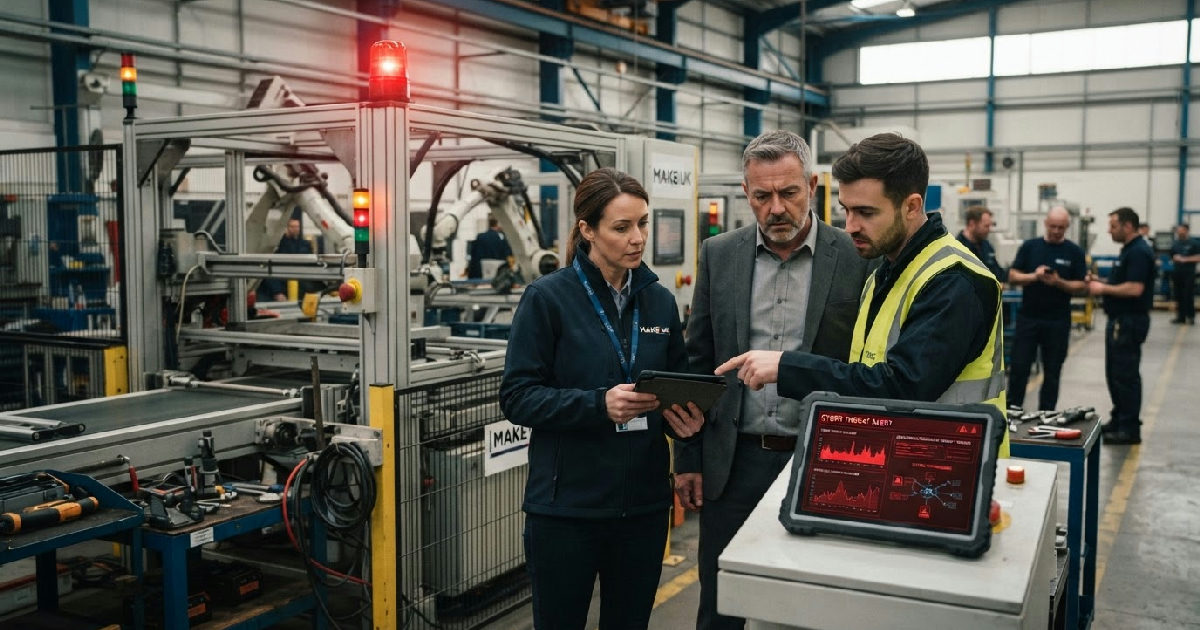
Nearly one-third of UK manufacturers have experienced a cyber incident in the last 12 months, either directly or through their supply chains, according to new research from Make UK. These attacks increasingly disrupt production, increase operational costs, and delay customer deliveries, pushing cybersecurity from a mere IT concern to a critical operational and business continuity risk.
The findings underscore a shift in how digital vulnerabilities manifest, often leading to tangible impacts on factory floors and supply chain integrity. This pervasive threat forces engineering and production leaders to reconsider their approach to digital defence against manufacturing cyber attacks.
The growing threat to factory floors and supply chains
Make UK’s report indicates that 30% of manufacturers experienced a cyberattack over the past year. When incidents occurred, production downtime and higher operational costs were the most frequent consequences for these firms.
The impact extends significantly through the supply chain. Of those affected by a supplier’s cyberattack, 31% reported delays in customer deliveries, while another 31% experienced reduced production capacity. Additionally, 23% faced supplier delivery delays, and the same percentage encountered shortages of critical components and materials.
High-profile cases illustrate this vulnerability. A significant disruption at Jaguar Land Rover, for instance, led to weeks of halted production across key UK manufacturing sites. This incident also generated wider impacts across its network of suppliers, demonstrating how quickly digital compromises can become physical roadblocks.
Financial fallout and operational disruption
The financial ramifications of these incidents are substantial, extending far beyond mere data breaches. Globally, the manufacturing sector has consistently ranked as the most targeted industry for cybercriminals, surpassing finance and healthcare.
Evidence suggests this targeting intensified between 2024 and 2025, with the number of manufacturers falling victim to cyberattacks nearly doubling. IBM’s X-Force 2025 Threat Intelligence Index highlights manufacturing as the most targeted industry for the fourth consecutive year.
Incidents like the MKS Instruments ransomware attack in February 2023 underscore the severe financial and operational impact. The major semiconductor equipment manufacturer saw a 20% decrease in quarterly revenue, representing more than $200 million in lost revenue as a result of encrypted systems and disrupted production.
Operations at some MKS facilities remained suspended for more than a month after the incident, affecting its $1.96 billion Vacuum Solutions and $1.06 billion Photonics Solutions divisions. The attack also created ripple effects, costing chipmaker Applied Materials an estimated $250 million.
Another example is Brunswick Corporation, which disclosed a significant cyberattack in June 2023. This incident forced the marine manufacturing giant to pause operations across its global facilities to contain the breach, highlighting the widespread nature of such threats.
The median cost of responding to a manufacturing ransomware attack, according to Arctic Wolf Incident Response teams, stands at $600,000. This figure only covers direct response and immediate recovery, often excluding the long-term impact on reputation and delayed projects.
Regulatory push for enhanced cyber resilience
Governments are increasingly recognising the systemic risk posed by manufacturing cyber attacks. The UK government estimates the annual cost of significant cyber attacks to UK organisations at £14.7 billion.
In response, the UK government launched its voluntary Cyber Resilience Pledge on July 7, 2026, at 10 Downing Street. This initiative aims to bolster the cyber resilience of UK organisations, building on a £90 million cash injection announced at the CYBERUK conference in April 2026.
Over 60 prominent businesses, including Marks & Spencer, Microsoft UK, and Vodafone Group, have already signed up for the pledge. These signatories commit to elevating cybersecurity to a board-level responsibility and implementing the NCSC’s Cyber Governance Code of Practice.
They also agree to register for the NCSC’s free Early Warning alert service and adopt a risk-based approach to Cyber Essentials certification across their supply chains. This includes using the Cyber Essentials Supplier Check Tool and conducting thorough audits to assess coverage.
Despite these efforts, adoption remains a challenge. As of 2025, only about 35,000 UK organisations out of more than five million held Cyber Essentials certification. This gap highlights the need for broader engagement, particularly among smaller and medium-sized enterprises.
Beyond national initiatives, a growing web of international regulations is shaping the cybersecurity landscape for manufacturers. The EU’s NIS2 Directive, adopted in 2023 and transposed into law in 2024, expands cybersecurity requirements to parts of the semiconductor supply chain operating in the EU.
Furthermore, the EU Cyber Resilience Act (CRA), set to take effect in September 2026, imposes mandatory cybersecurity requirements for products with digital elements. This regulation aims to ensure products are secure by design throughout their lifecycle, covering aspects like mandatory certification and vulnerability disclosure.
The UK’s Product Security and Telecommunications Infrastructure (PSTI) Act, already in force, mirrors some aspects of the CRA, indicating a converging global regulatory trend. These frameworks will compel manufacturers to embed cybersecurity into their engineering and product development processes.
Make UK’s call for action and strategic shifts
Nina Gryf, Innovation and Digitalisation Lead at Make UK, emphasised that cyberattacks are no longer abstract events.She stated, “They are showing up on the factory floor through downtime, higher costs, delayed orders and pressure on supply chains.”
Gryf contends that in a connected industrial economy, a digital weakness quickly translates into a production problem. She argues that “cyber resilience is business resilience,” urging firms to focus on clear leadership, basic controls, and tested recovery plans.
Jonathon Ellison, Director of National Resilience at the National Cyber Security Centre (NCSC), echoed this sentiment. He stressed that “no manufacturer can afford to treat cyber security as anything other than a business-critical priority” in today’s threat landscape.
The NCSC actively supports organisations of all sizes in strengthening their cyber defences, offering resources from board-level governance training to practical services like Early Warning and Exercise in a Box. This collaborative approach aims to elevate the overall security posture of the sector.
Make UK’s report offers practical steps for manufacturers to bolster their defences. These include board-level ownership of cyber risk, comprehensive employee training, and robust incident response planning. Such measures are crucial for mitigating the impact of an attack.
Further recommendations focus on diligent patch management, rigorous supplier assurance protocols, and the protection of operational technology systems. These preventative and reactive strategies are vital for maintaining continuous production.
Ensuring senior leadership responsibility for cybersecurity is another key recommendation, with the report noting that 45% of manufacturers have assigned responsibility for this area. However, 17% lack cyber insurance and 16% are unsure of their coverage, indicating significant gaps in risk mitigation.
Engineering cyber resilience into operations
The increased frequency and sophistication of manufacturing cyberattacks demand that engineering departments integrate cybersecurity into every phase of their operations.. This goes beyond IT infrastructure to encompass the precision manufacturing processes and industrial control systems themselves.
Legacy operational technology (OT) systems, often designed without modern cybersecurity threats in mind, present unique vulnerabilities. Manufacturers must implement robust segmentation, continuous monitoring, and threat detection specifically tailored for OT environments.
Furthermore, the growing adoption of automation, robotics, connected machinery, enterprise systems, and remote access tools introduces new attack vectors. Engineers are now tasked with ensuring these advanced digital systems are secure by design, with cybersecurity considerations influencing everything from PLC programming to remote access protocols.
This holistic approach means cybersecurity can no longer be an afterthought or a separate department’s problem. It must be an inherent consideration in system architecture, equipment procurement, and process design. Secure design principles extend to every aspect of an industrial facility, from initial investment and construction to ongoing operations.
The implications for supply chain engineering are also profound. Securing these intricate networks involves not only physical infrastructure but also the establishment of rigorous digital trust with every supplier and partner. This requires continuous auditing and contractual enforcement of cybersecurity standards, ensuring comprehensive protection against evolving threats.
